


PokerTracker website hacked
Users who entered credit card information between December 23 and January 2 could potentially be impacted by the attack.
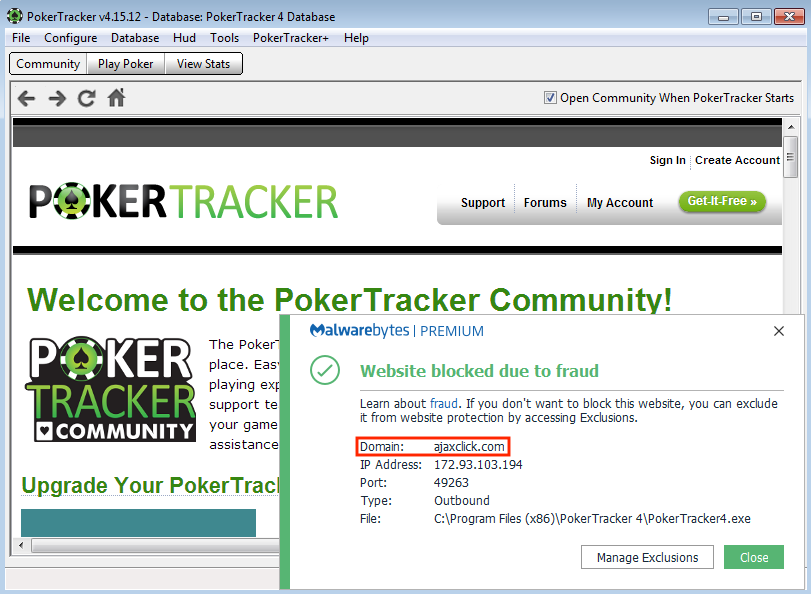
Last week MalwareBytes revealed that the website for PokerTracker had been hacked and loaded with a 'Magecart' script, which is a code that steals payment information from customers. This is the script best known for high profile cyberattacks of British Airways and Ticketmaster.
Yesterday Derek Charles of PokerTracker announced that they were made aware of the attack on August 8. They determined it was made possible because they were running an outdated version of the Drupal CMS. Steps were immediately taken to disable the script, update their software and tighten up their security.
The attack took place between December 23, 2018 and January 2, 2019. Any customers who entered their credit card information on the PokerTracker website during that time are being contacted and urged to monitor their credit card accounts for fraudulent activity. Derek Charles estimated the number of potentially affected customers was in the low thousands.
PokerTracker does not save credit card or billing information on their servers. The PokerTracker application itself has not been impacted, only their website. Username and password information is unlikely to have been compromised however PokerTracker still recommend changing your password to be on the safe side.
In his statement on 2+2, Derek Charles apologised for the length of time it took to respond to these attacks:
We regret that this incident has occurred and sincerely apologize that it has taken us three weeks to properly assess the scope and severity of the damage to notify potentially affected customers. This is the first time that we have had a major security incident and we have learned a lot during this process that we can improve upon.
